Information and Communication Technology

Independent expertise for reliable, secure and connected technology

ICT organizations develop and manage digital infrastructures, software, networks, connected products and communication systems. This technology forms the foundation for business processes, industrial applications and public services. As a result, requirements related to information security, cybersecurity, reliability, interoperability and compliance are also increasing.

DEKRA supports ICT service providers, software companies, manufacturers of connected products and other technology organizations with independent audits, certification, cybersecurity testing and product testing. Our experts assess both organizational processes and management systems, as well as the technical security and performance of digital products and systems. In this way, we help organizations manage risks, demonstrate compliance and gain access to national and international markets.
DEKRA's expertise for ICT
Independent cybersecurity expertise

Our experts conduct audits, penetration tests and technical cybersecurity assessments. This gives organizations objective insight into vulnerabilities, control measures and the effectiveness of their information security.

Organization and technology

DEKRA assesses management systems and business processes as well as digital products, software and connected systems. This enables organizational and technical risks to be evaluated from one integrated perspective.

Support for compliance and market access

Audits, testing and certification help organizations demonstrate that their processes and products meet relevant standards, legislation and market requirements. This strengthens the confidence of customers, clients and other stakeholders.

Internationally recognized expertise

DEKRA combines testing facilities and sector expertise in the Netherlands with a global network of laboratories, auditors and cybersecurity specialists. This enables us to support organizations with both local and international challenges.

Featured services for ICT

  • ISO 27001 certification
    ISO 27001 certification demonstrates that an organization manages information security risks systematically. DEKRA assesses, among other things, documentation, risk analysis, control measures and the effective operation of the Information Security Management System.
  • IT service management and privacy information management
    DEKRA also certifies organizations according to standards such as ISO 20000-1 and ISO 27701. These standards help ICT organizations manage the quality of their IT services and address privacy risks systematically within their management systems.
  • Penetration testing
    Our cybersecurity experts conduct penetration tests on networks, web applications, mobile applications and digital products, among other things. This makes vulnerabilities and weaknesses visible before they can be exploited.
    Organizations that provide penetration testing services can obtain certification from DEKRA under the CCV Pentesting certification scheme. This certification provides clients with independent assurance regarding the expertise, reliability and working methods of the penetration testing service provider.
  • Cybersecurity for connected products
    DEKRA tests and assesses the cybersecurity of connected products, components and industrial systems. Our services include penetration testing, assessments in accordance with IEC 62443 and testing against cybersecurity requirements under the Radio Equipment Directive.
EMC testing

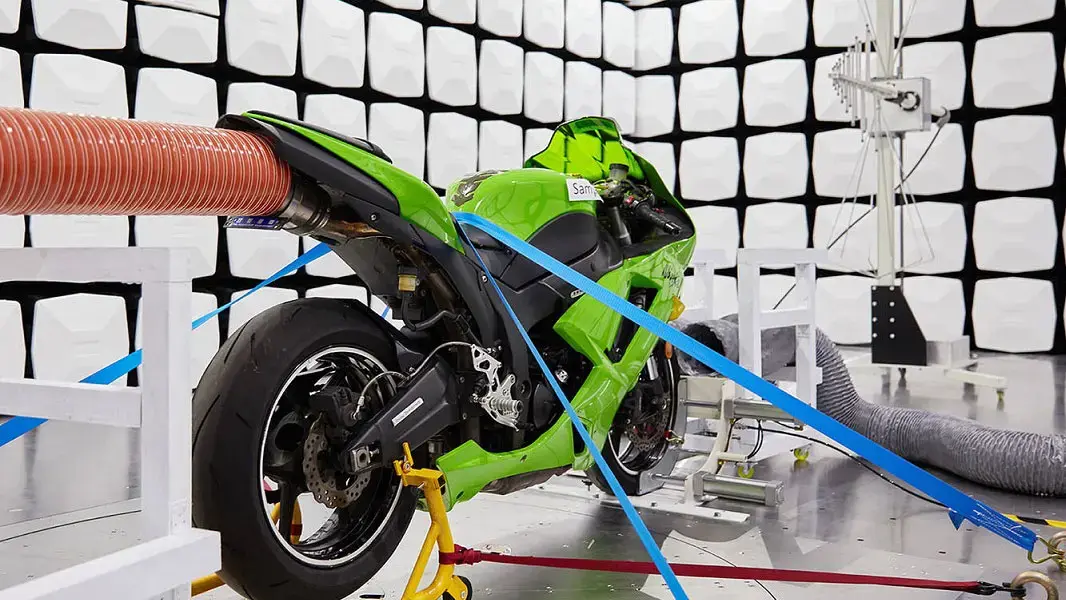
Electromagnetic Compatibility Testing (EMC)
Laboratory and on-site compatibility testing to determine the compliance of electronic components and products with regulatory electromagnetic standards.
Details
Global market access service logistic options

Global Market Access service

Meet technical regulations with certifications and approvals so your organization can easily enter global markets.
Details
Green coding screen

IEC 62443

IEC 62443 is specifically focused on the security of industrial communication networks and systems. These standards address both technical and procedural aspects of industrial automation and control systems (IACS).
Details
Certification information security

Information security

Certification of your information security demonstrates that you are dealing with (digital) data exchange and storage carefully, and guarantees the quality of your IT processes.
Details
Man and woman inspect a server unit

ISO 20000-1 certification

ISO 20000-1 certification is proof that your IT service management systems meet international quality standards. You demonstrate that your IT services are reliable, efficient and customer-oriented.
Details
certification ISO 27001

ISO 27001 certification

Demonstrate that information security is a high priority within your organization with the ISO/IEC 27001 certification.
Details
ISO 27701 certification at DEKRA.

ISO 27701 certification

With an ISO 27701 certificate, your organization demonstrates control over privacy requirements when processing (personal) data.
Details
password security laptop

Pentesting

Pentesting (also known as penetration testing) helps organisations identify and fix vulnerabilities in their IT systems.
Details
Certification and marks

Product certification and marks for products
Recognized distinctions with industry certifications and regulatory marks demonstrating product safety, performance and quality standards in global markets.
Details
Quality Management certification

Quality Management certification

Each industry has specific requirements for a quality management system. With our certification, you can be sure that your quality system meets the right standards.
Details
RF testing

Radiofrequency (RF) testing

Electronic device and component testing to verify wireless interface compliance with relevant standards and requirements for uninterrupted world market access.
Details
RED directive eu

RED Directive testing

You must comply with the Delegated Act of the Radio Equipment Directive (RED) from August 2025. Read more about future legislation and how DEKRA can help you here.
Details
/>

Digital reliability from a single organization

DEKRA combines expertise in management systems, information security, cybersecurity, product safety, EMC and wireless technology. This enables ICT organizations to have both their internal processes and their digital products and systems assessed independently. The resulting objective information helps them reduce risks, demonstrate compliance and strengthen confidence in their technology.
Global services
In addition to our services in the Netherlands, DEKRA supports ICT organizations, technology companies and manufacturers worldwide with audits, certification, cybersecurity assessments, connectivity testing and product testing. Our international network of laboratories and experts works with internationally recognized standards and consistent assessment methods. In this way, we combine local market knowledge with support for global compliance and market access.

Frequently Asked Questions

DEKRA supports software companies, IT service providers, hosting providers, telecommunications organizations, manufacturers of connected products and providers of digital infrastructure, among others. Our services are tailored to the processes, products, markets and standards relevant to each organization.
ISO 27001 provides a structured management system for identifying and managing information security risks. Through independent certification by DEKRA, an organization can demonstrate that appropriate organizational and technical measures have been implemented and are being applied effectively.
Yes. DEKRA conducts penetration tests on applications and networks, among other things, and also tests physical, electronic and wireless products. Depending on the product, the assessment may cover cybersecurity, product safety, EMC, RF and relevant market access requirements.
Independent assessment provides objective evidence that processes, systems or products meet relevant requirements. This helps ICT organizations manage risks, comply with customer and contractual requirements, gain market access and build trust with customers and other stakeholders.